LLM & AI agent penetration testing
Our testing follows the OWASP Top 10 for LLM Applications and MITRE ATLAS, extended with our own attack research:
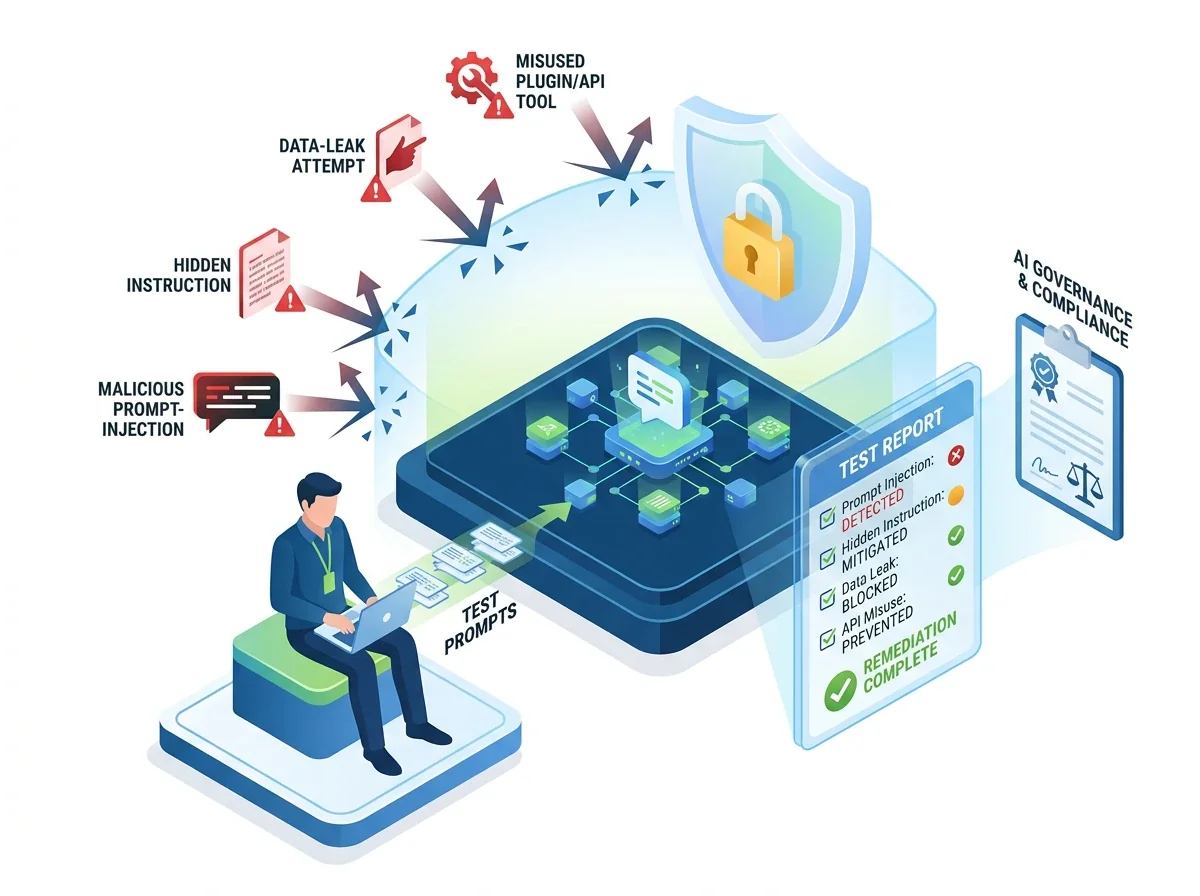
Prompt injection
Direct and indirect injection via documents, emails, web pages and tool outputs.
Data leakage
Extraction of system prompts, training data, PII and other users’ content.
Agent & tool misuse
Abuse of plugins, APIs and excessive permissions to take unauthorised actions.
Jailbreaks & guardrail bypass
Testing content filters and safety controls against current techniques.
Infrastructure
The surrounding app, APIs, vector databases, authentication and hosting.
Clear remediation
Prioritised findings with practical fixes, followed by a retest.
AI governance & compliance
We already help organisations implement ISO 27001. We bring the same practical approach to AI governance:
- ISO/IEC 42001 AI management system gap analysis and implementation
- EU AI Act risk classification and readiness
- AI acceptable-use policies and staff awareness training
- AI risk assessments and vendor/model due diligence