Turning logs into useful information
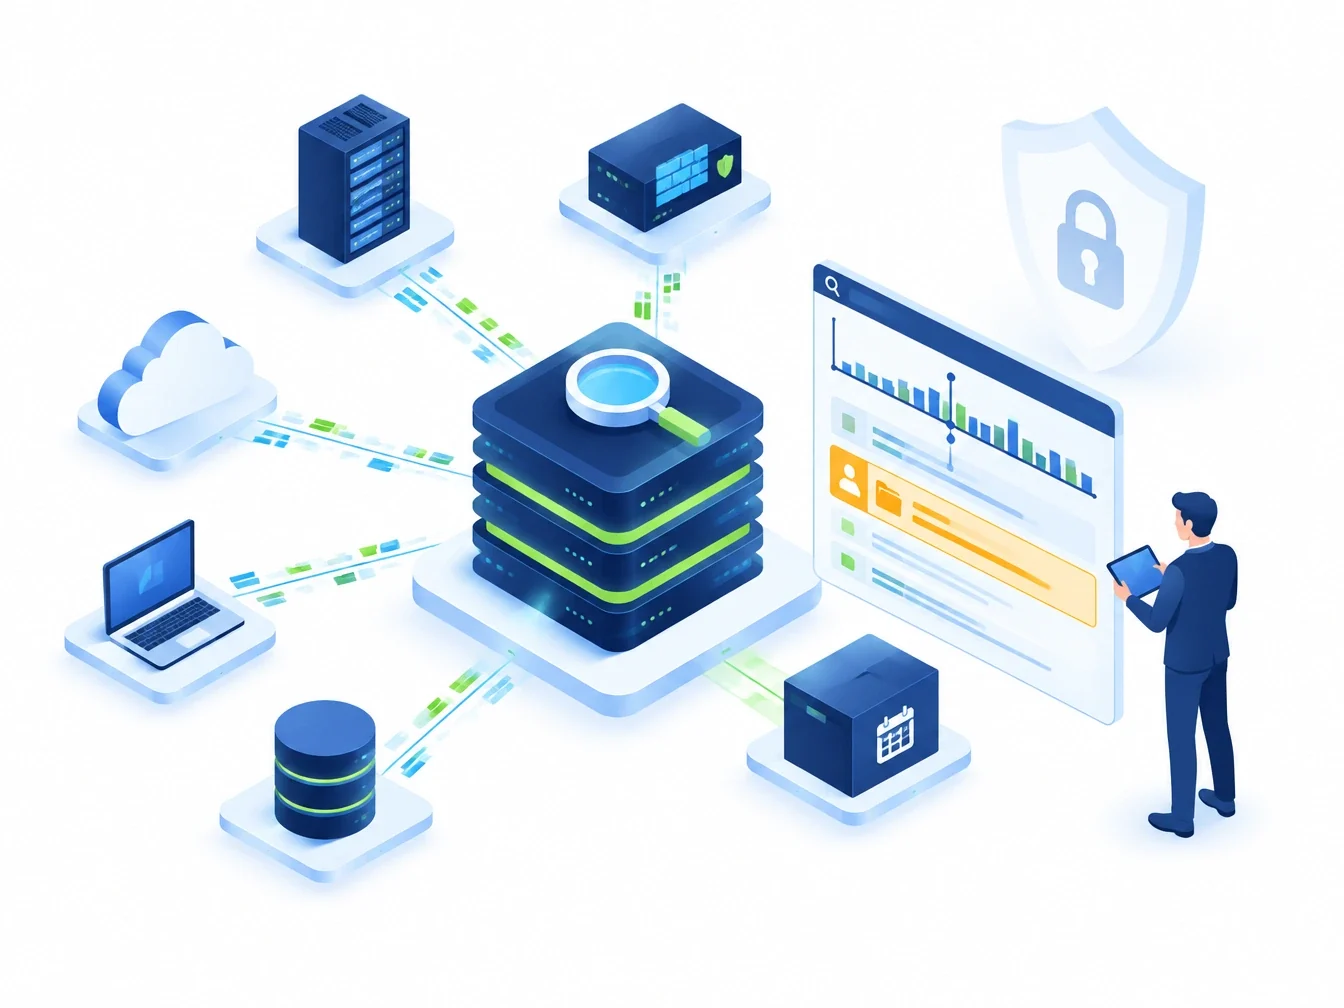
We provide a variety of correlation techniques that integrate different sources and turn organisational data into useful information. Big data covers a broad spectrum of use cases, including data analytics, so we always take your individual business and situation into account.
Our solution monitors privileged users, admin users, unknown users on the network, external users, suspicious behaviour, and escalation of user rights. Libraries and directories are typically monitored. The most common use cases show who accessed, changed, deleted, uploaded, downloaded or copied a specific file.
Why log monitoring matters
Log monitoring is vital to an effective information security programme. Monitoring activity across your security infrastructure and critical information assets lets you quickly identify and thwart malicious activity. It also satisfies industry regulations that require log monitoring, and improves the return on your security investments.
- Automatically indexes all data, including complex multi-line application logs
- Search everything without custom connectors or database-schema limitations
- Stores security records in sufficient detail for an appropriate period
- Supports auditing, forensic analysis and internal investigations
- Establishes baselines and identifies operational trends and long-term problems
Logs were once used mainly for troubleshooting. Today they also help optimise system and network performance, record user actions, and provide the data needed to investigate malicious activity.