Incident response and handling procedures, including determining the source of an incident and carrying out digital forensics investigations, are among the top services we offer. We believe it is vital to evaluate every incident and document its root cause.
Don’t destroy the evidence
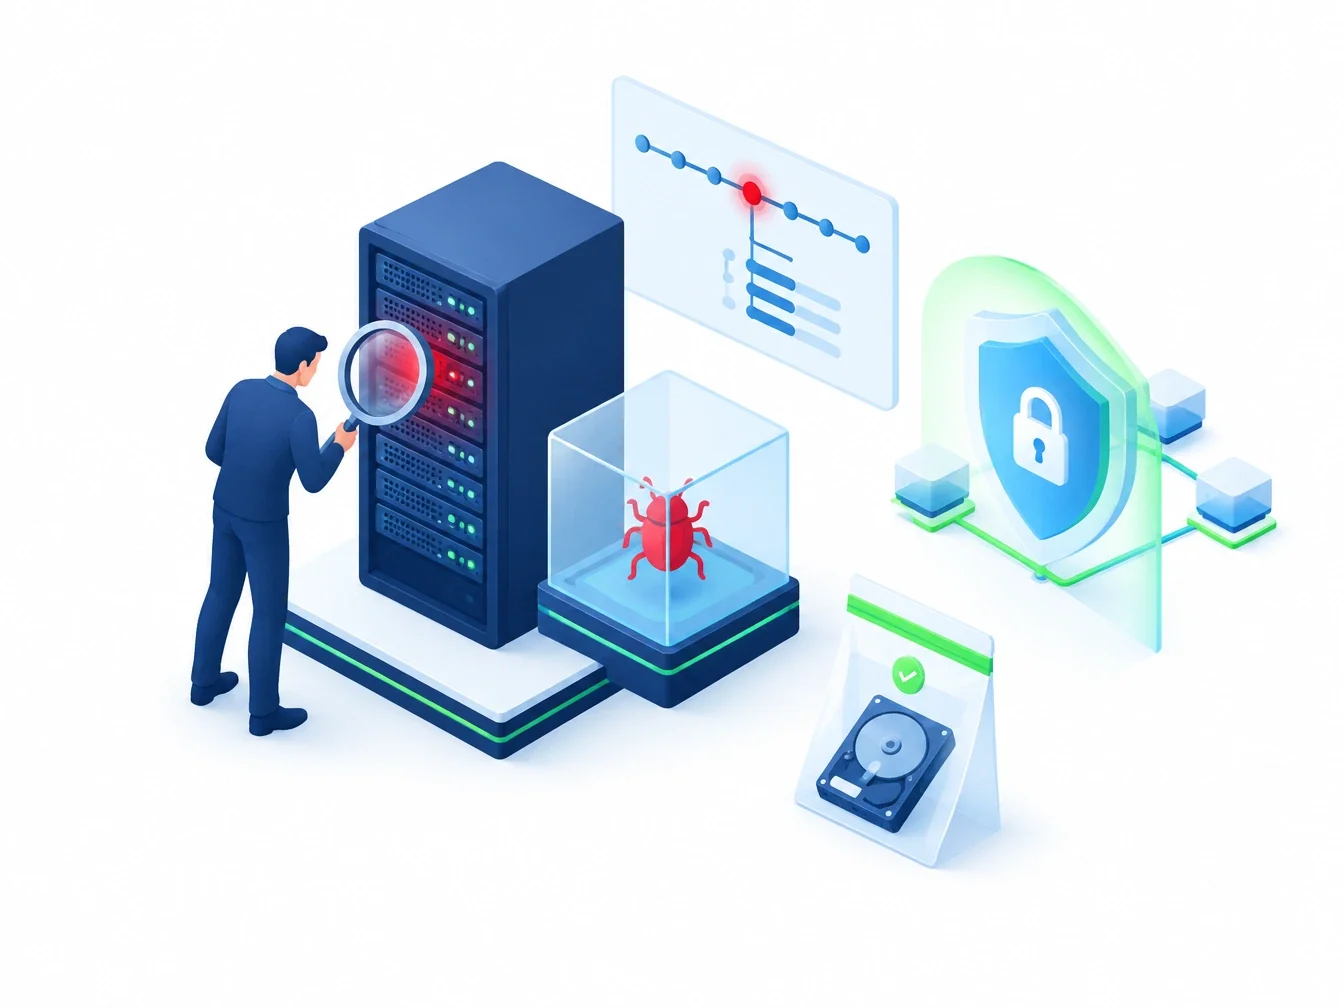
Forensic artefacts can be lost simply by IT staff cleaning compromised machines. Just because a virus or Trojan was detected does not mean it wasn’t already running undetected and exfiltrating data. Eon IT provides full static and dynamic malware analysis, including sandbox analysis.
Advanced persistent threats
Advanced Persistent Threats (APTs) are among the most common vectors for malware infection. These attacks are highly customised towards the financial and digital assets of today’s businesses, and they exploit weaknesses in both people and technology. The biggest institutions and governments have been hacked and taken a long time to notice. Attackers already inside the gate are much harder to control and track because they use assigned privileges and roles to obtain and exfiltrate information. Our unique skill set lets us track and quarantine the threat.
What our investigation covers
- Examining log reports and comparing backups to identify modifications to the network
- Investigating the introduction of foreign software tools to identify intruders
- Determining the extent to which the network has been compromised
- Mitigating potential damage from the intrusion
- Documenting corrective actions and confirming that no backdoor has been planted